Managed IT Services for Restaurants: A Multi-Site IT Blueprint
Managed IT services for restaurants help multi-location groups standardize infrastructure, strengthen cybersecurity, and gain centralized visibility.
Key Takeaways
- Multi-location restaurant growth is easier to support when each new location deploys against a documented IT and security baseline instead of starting with a bespoke design.
- Site-by-site technology decisions create configuration drift, inconsistent controls, fragmented visibility, and growing documentation requirements.
- Standardization and customization can coexist. Location-specific requirements should be treated as governed exceptions within a common architecture.
- Centralized visibility is necessary after deployment because it shows whether controls remain operational across the restaurant portfolio.
- A repeatable restaurant security blueprint should define technology standards, ownership, monitoring, escalation, evidence, and reporting before opening day.
- A managed services partner should unify IT operations and restaurant cybersecurity with clear accountability instead of creating another vendor handoff.
Managed IT services for restaurants should give every location a documented technology and security baseline, centralized visibility, and one accountable operating model. For growing restaurant groups, that standardization reduces configuration drift, makes new openings repeatable, and helps leadership verify that controls are working across the portfolio.
This article explains how multi-location restaurant IT standardization works, why site-by-site builds create risk, what a security blueprint should contain, and how to evaluate a partner that can support restaurant cybersecurity without sacrificing legitimate location-specific flexibility.
What is multi-location restaurant IT standardization?
Multi-location restaurant IT standardization is the use of a documented, repeatable technology and security baseline across every restaurant location, with defined rules for approved local variations.
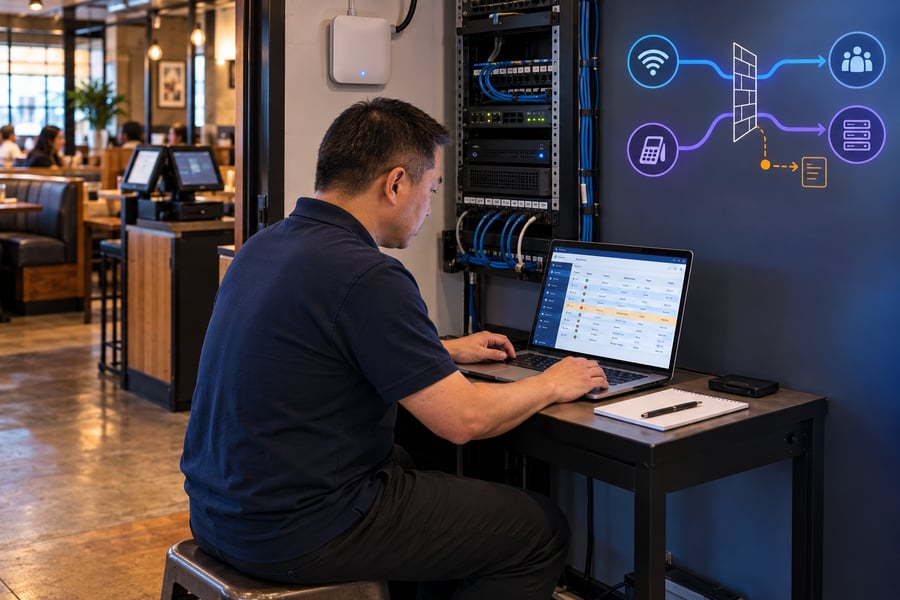
That baseline should cover core network architecture, wireless infrastructure, endpoints, identity, firewalls, monitoring, incident response, documentation, and ownership. The goal is not simply to standardize products. It is to standardize how technology is configured, secured, operated, and supported.
Standardization does not mean every restaurant must be identical; it means every approved variation is deliberate, documented, and managed within a common control framework.
Why does site-by-site restaurant IT create risk?
Site-by-site restaurant IT creates configuration drift, fragmented visibility, inconsistent controls, and more manual work as the restaurant group grows.
Opening deadlines often encourage local exceptions and one-off decisions. Those choices may solve an immediate problem, but they accumulate across a portfolio.
|
Operating area |
Site-by-site model |
Standardized model |
|
New openings |
Technology redesigned under deadline |
Approved baseline deployed |
|
Visibility |
Site-level tools and logs |
Centralized oversight |
|
Documentation |
Completed after deployment or manually |
Built into the operating model |
|
Exceptions |
Local and inconsistently governed |
Documented and controlled |
|
Accountability |
Distributed across teams or vendors |
Defined ownership |
The staffing burden extends beyond hospitality. Splunk’s 2026 downtime research found that 89% of technology leaders cited significant staffing requirements for resolving incidents. Among organizations with the lowest downtime costs, 98% said end-to-end visibility was very or extremely important.
Forrester also projected that 75% of technology decision-makers would see technical debt rise to a moderate or high level of severity by 2026 as new AI solutions add complexity to IT environments. The finding is not restaurant-specific, but it reinforces the broader cost of adding technology without disciplined architecture and governance.
What should a standardized restaurant IT platform include?
A standardized platform turns the opening checklist from a series of design decisions into deployment against an approved baseline. A repeatable restaurant cybersecurity baseline should address:
- Network segmentation, switching, Wi-Fi, and connectivity standards
- Identity and access management with multi-factor authentication
- Endpoint detection and response plus vulnerability management
- Managed firewall, email, and cloud security requirements
- Continuous monitoring and documented incident-response procedures
- Configuration records, runbooks, and compliance evidence
Standardization can still accommodate the physical differences between restaurants. Cameron Mitchell Restaurants used Logically, Extreme Networks, and SonicWall to create a more consistent network and security foundation across 74 locations while retaining flexibility for individual layouts.
Orlando Sprockel, Senior Director of IT, summarized that balance: “It’s not just plug-and-play. We can customize everything for each restaurant.”
How does centralized visibility reduce multi-site risk?
Centralized visibility lets IT and security teams confirm whether controls are operating across all locations, investigate issues in context, track remediation, and produce evidence without collecting site-level logs manually.
Deployment confirms what was installed. Ongoing visibility shows what is operating now, including changes introduced through patches, vendor integrations, firewall modifications, endpoint activity, or local administration.
Logically’s current managed cybersecurity services include continuous monitoring, SecureCare managed detection and response powered by SentryXDR, and expert-led response. Logically’s governance, risk, and compliance services add control validation, audit evidence support, and executive risk visibility.
What should a restaurant security blueprint include?
A restaurant security blueprint should define network architecture, identity and access controls, endpoint protection, firewall policy, monitoring, incident response, compliance evidence, ownership, and escalation paths before a location opens.
A practical blueprint also defines how those requirements move from design into operations:
- Design: Establish the approved architecture, control baseline, responsibilities, and compliance requirements.
- Pilot: Validate the blueprint at a representative location before broad deployment.
- Deploy: Configure each opening against the approved standard and document any exceptions.
- Monitor and respond: Begin IT and security monitoring when the site goes live, with defined escalation paths.
- Report and improve: Track remediation, operating trends, control evidence, and lessons that should update the baseline.
This turns restaurant cybersecurity from a set of products into an operating discipline with defined ownership.
Who benefits most from a standardized multi-site model?
The strongest fit is a restaurant group with five or more locations, lean centralized IT resources, high uptime dependency, and a willingness to standardize core infrastructure while allowing controlled site-specific needs.
This model is particularly relevant when expansion, POS reliability, vendor sprawl, ransomware exposure, limited IT bandwidth, or inconsistent network and security practices have become recurring management concerns.
How should restaurant groups evaluate managed IT services for restaurants?
Restaurant groups evaluating managed IT services for restaurants should look beyond help desk coverage and ask whether the provider can support the entire operating model.
Evaluate whether the provider can:
- Standardize infrastructure while governing legitimate site exceptions
- Integrate restaurant cybersecurity and IT operations instead of separating responsibility
- Monitor and support distributed environments around the clock
- Support PCI DSS-related technology and evidence requirements
- Provide centralized reporting, documented ownership, and clear escalation paths
Logically’s current approach unifies IT operations and cybersecurity under a single, accountable operating model with shared visibility and coordinated response. That model is designed to reduce the handoffs and ownership gaps that become harder to manage as the number of locations grows.
How can restaurant groups scale without multiplying IT risk?
The right managed IT services for restaurants turn each opening into a repeatable deployment, not a fresh design exercise. For multi-location restaurant IT, the practical test is whether leadership can verify control posture across every site without assembling evidence manually.
A standardized restaurant cybersecurity and IT blueprint gives growth a governed foundation: defined architecture, continuous visibility, controlled exceptions, and accountable ownership.
For a real-world example, see how a 74-location restaurant group created a more consistent and scalable technology environment in the Cameron Mitchell Restaurants network modernization case study.
Download the Cameron Mitchell Restaurants Case Study today!
By Todd Barrett, Director, Cybersecurity Sales, Logically
FAQs
What is multi-location restaurant IT standardization?
Multi-location restaurant IT standardization is the use of a documented, repeatable technology and security baseline across every restaurant location, with defined rules for approved local variations.
Why is site-by-site restaurant IT risky?
Site-by-site restaurant IT creates configuration drift, fragmented visibility, inconsistent controls, and more manual work as the restaurant group grows.
Can standardized restaurant IT still support location-specific needs?
Standardization does not mean every restaurant must be identical; it means every approved variation is deliberate, documented, and managed within a common control framework.
How does centralized visibility help restaurant groups?
Centralized visibility lets IT and security teams confirm whether controls are operating across all locations, investigate issues in context, track remediation, and produce evidence without collecting site-level logs manually.
What should a restaurant security blueprint include?
A restaurant security blueprint should define network architecture, identity and access controls, endpoint protection, firewall policy, monitoring, incident response, compliance evidence, ownership, and escalation paths before a location opens.
Which restaurant groups are the best fit for standardized managed IT?
The strongest fit is a restaurant group with five or more locations, lean centralized IT resources, high uptime dependency, and a willingness to standardize core infrastructure while allowing controlled site-specific needs.